Cyber Essentials has become an important requirement for many organisations. Whether driven by customer expectations, procurement requirements, supplier assurance, or internal security objectives, certification is increasingly used as evidence that baseline cyber security controls are in place.
At ServQual, we support organisations through the Cyber Essentials readiness and certification process as an IASME Consortium-accredited Cyber Essentials Certification Body.
According to the UK Government’s Cyber Security Breaches Survey 2025/2026, 43% of UK businesses and 28% of charities identified a cyber security breach or attack during the previous 12 months. Strong cyber security foundations are no longer a nice-to-have. They are increasingly expected by customers, suppliers, and stakeholders.
Understanding Your Current Position
One of the biggest challenges organisations face is understanding where they currently stand.
Before certification, organisations often need greater visibility of:
- Assets and devices within scope
- User access arrangements
- Cloud and hybrid environments
- Existing security controls
- Areas of potential cyber risk
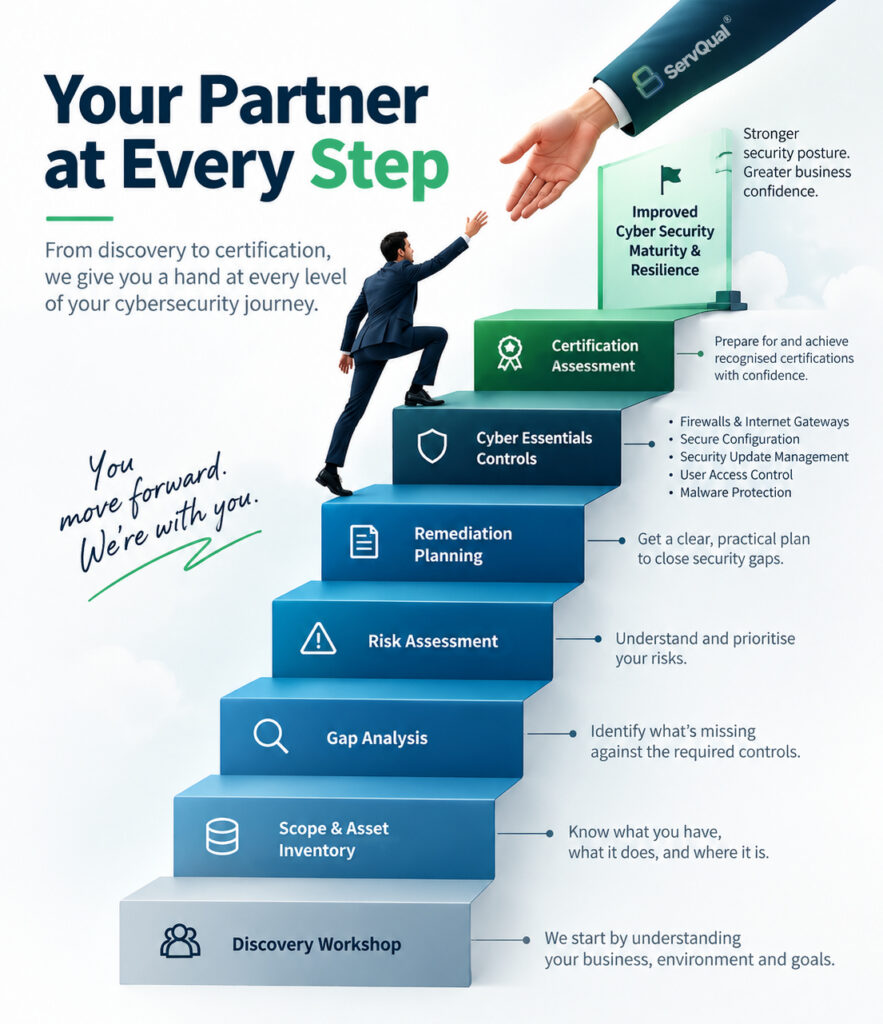
Through discovery workshops, scope reviews, and Cyber Essentials gap analysis, ServQual helps organisations establish a clear starting point and identify priorities for improvement.
Identifying Gaps and Reducing Risk
Cyber Essentials is built around a recognised set of controls designed to reduce exposure to common cyber threats and establish a practical cyber security baseline. The scheme is overseen by the National Cyber Security Centre (NCSC) and delivered by IASME Consortium.
In our experience, the challenge is often not the assessment itself.
The challenge is understanding ownership, visibility of assets, consistency of security controls, and the practical risks that exist across the organisation. These are frequently the same issues that affect wider cyber security, compliance, governance, and operational resilience initiatives.
Our role is not simply to assess requirements. We help organisations understand where gaps exist, how those gaps translate into risk, and what actions should be prioritised to strengthen security outcomes.
Why Organisations Engage ServQual
Many organisations begin their Cyber Essentials journey expecting a certification exercise and leave with a much clearer understanding of their environment, security controls, and areas of risk.
Discovery workshops, gap analysis, and risk assessments often uncover opportunities to strengthen governance, improve accountability, and enhance operational resilience beyond the requirements of the assessment itself.
For organisations working with UK customers, public sector supply chains, regulated industries, or security-conscious clients, Cyber Essentials can help provide recognised assurance that appropriate cyber security controls are in place.
The certificate is important. The insight gained during the journey is often where the greatest long-term value is realised.
Supporting Certification with Confidence
ServQual supports organisations throughout the Cyber Essentials process through:
- Discovery Workshops
- Scope Reviews
- Cyber Essentials Gap Analysis
- Risk Assessments
- Remediation Planning
- Certification Services
Our objective is straightforward: help organisations achieve Cyber Essentials certification while strengthening cyber resilience, improving security maturity, and reducing risk across the organisation.
"Cyber Essentials is more than a certification milestone. It is a practical foundation for strengthening cyber resilience, reducing risk and building trust with customers and partners."

Dara Sturgeon
Security Success Manager/ GRC Manager | ServQual
FAQ
Most frequent questions and answers
Cyber Essentials is a UK Cybersecurity certification scheme designed to help organisations establish a practical baseline of security controls and reduce exposure to common cyber threats. The scheme is overseen by the NCSC and delivered by IASME Consortium.
ServQual supports organisations through discovery workshops, scope reviews, Cyber Essentials gap analysis, risk assessments, remediation planning and certification services.
The Cyber Essentials journey in the draft focuses on firewalls and internet gateways, secure configuration, security update management, user access control and malware protection.
Start by understanding the systems, assets, users, cloud environments and controls in scope. ServQual can then help identify gaps, prioritise remediation and prepare the organisation for certification.
The draft states that ServQual supports organisations through the Cyber Essentials readiness and certification process as an IASME Consortium-accredited Cyber Essentials Certification Body. This exact accreditation wording should be kept only if it matches ServQual’s official approval documentation.
No. Cyber Essentials provides a baseline, while wider Cybersecurity, governance, compliance and operational resilience activities may require additional controls and ongoing review. The draft itself positions Cyber Essentials as a foundation that can support broader security and resilience improvements.
ServQual can help identify where gaps exist, explain how those gaps translate into risk and prioritise actions for improvement before progressing through certification.
The draft identifies customer expectations, procurement requirements, supplier assurance and internal security objectives as common drivers for certification.
Ready to Achieve Cyber Essentials?
Strengthen your Cybersecurity baseline, identify gaps and progress through Cyber Essentials certification with ServQual.
Note: Certification is subject to the applicable Cyber Essentials scheme requirements, assessment scope, and successful completion of the certification process. ServQual does not guarantee certification outcomes.