CSPM reduces attack surface exposure by continuously inventorying resources across AWS, Azure, GCP and Kubernetes, evaluating each against a codified baseline, and routing deviations to remediation with business context attached. The problem it solves is that cloud attack surface is created declaratively by IaC, console changes and API calls and expands faster than periodic assessment can track.
An effective programme has five elements: authoritative multi-cloud inventory; a policy-as-code baseline mapped to ISO 27001, NIST CSF 2.0, CIS v8 and CSA CCM; risk-based prioritisation combining exposure, identity blast radius and data sensitivity; remediation shifting left into pipelines and right into guarded automation; and continuous evidence for audit. CSPM is one layer of a CNAPP, complementing CWPP, DSPM, CIEM and external Attack Surface Management.
Executive Summary
Cloud Security Posture Management (CSPM) continuously discovers cloud resources, evaluates their configuration against a codified control baseline, and drives deviations to closure before they become exploitable. It keeps the reachable and over-permissioned surface of a cloud estate within a governed tolerance.
The problem is structural. Cloud shifts the dominant failure mode of enterprise security from unpatched perimeter software to declarative configuration error. A single parameter a bucket policy, a security group rule, a wildcard IAM trust relationship, a public Kubernetes API endpoint can create an internet-reachable path to regulated data in seconds, with no exploit code written. Under shared responsibility, providers secure the cloud and customers secure what they build in it; CSPM is the assurance mechanism for the customer half.
Business value. CSPM converts an unbounded estate into a measurable risk surface, answering the three questions boards ask: what do we own, what is exposed, how fast do we close it. Mean time to remediate becomes a reportable key risk indicator.
Security value. MITRE ATT&CK cloud techniques public-facing application exploitation, valid cloud accounts, infrastructure discovery depend disproportionately on configuration weakness. Eliminating exposure is cheaper than detecting its abuse.
Compliance value. One control evaluation can evidence ISO/IEC 27001 Annex A, NIST SP 800-53, CIS Controls v8, SOC 2, PCI DSS and the CSA Cloud Controls Matrix simultaneously the shift from point-in-time sampling to Continuous Controls Monitoring.
CSPM is a governance loop, not a product you buy and finish: discover, assess, prioritise by exploitability and business context, remediate at the infrastructure-as-code source of truth, prove closure. Treated as a dashboard it accumulates findings; treated as a control system it reduces exposure.
Problem Statement: Why Cloud Attack Surface Outruns Enterprise Control
In a datacentre, provisioning required procurement, physical access and change advisory approval. Those frictions were, incidentally, security controls. Cloud removed them: any engineer with sufficient IAM permissions can instantiate a public load balancer or database endpoint in under a minute via API, with no review. Attack surface is now a function of permissions and pipeline velocity.
Business and operational pain. Estates grow through acquisition, shadow IT and team autonomy, so there is no defensible answer to “what do we own?” Findings live in provider consoles while risk lives in a register, so exposure never reaches the board in actionable form. Default policy packs produce tens of thousands of undifferentiated findings that are consequently ignored, untagged resources are unassignable, and console fixes to IaC-managed resources recur at the next apply.
| Security Gap | Manifestation | Consequence |
|---|---|---|
| Unknown internet exposure | Public object storage, 0.0.0.0/0 ingress, public DB endpoints | Data access without exploitation |
| Identity over-permissioning | Wildcard policies, unconstrained trust, static keys | Lateral movement, privilege escalation |
| Logging blind spots | Audit logging disabled; no data-plane logging | Undetectable activity; failed forensics |
| Unmanaged encryption | Unencrypted volumes and snapshots; weak key policy | Regulatory notification exposure |
| Control-plane exposure | Public Kubernetes API, open management ports, no MFA | Direct control-plane compromise |
Compliance and governance. GDPR Article 32 requires regular testing of control effectiveness; India’s DPDP Act 2023 obliges Data Fiduciaries to implement reasonable security safeguards; NIS2 places risk-management accountability on management bodies. None is satisfied by annual review. Governance failures are consistent: policy exists in documents but not code, exceptions are informal and unexpiring, and no owner exists for posture as distinct from cost.
Industry direction. Identity has become the cloud perimeter, tooling is consolidating into CNAPP, and AI-assisted development raises the rate at which insecure defaults reach production absent automated guardrails.
Validate quantitative figures against current primary sources the Verizon DBIR, IBM Cost of a Data Breach, or Gartner and Forrester research rather than secondhand statistics.
Diagram 1 Attack Surface Expansion Drivers
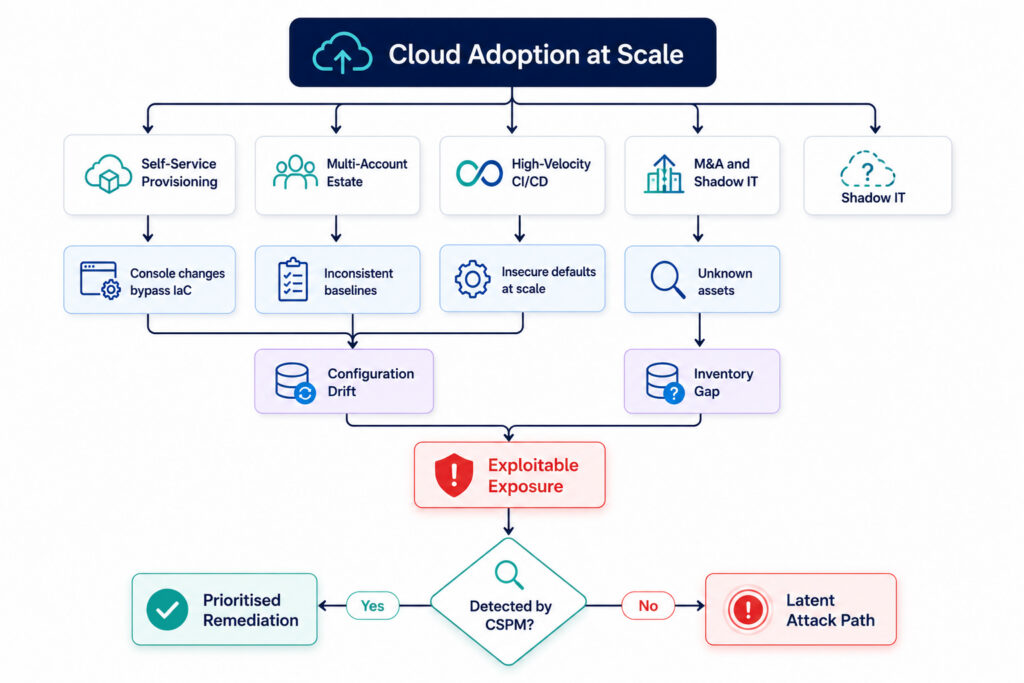
Why it matters: scanning only IaC misses console drift; scanning only runtime misses the pipeline that recreates the flaw.
Why This Matters: Resilience, Liability and Board
Accountability
Resilience. Misconfiguration causes outages as often as breaches; a mis-scoped key policy can take production offline immediately. Baselines covering multi-AZ configuration, backup enablement and deletion protection serve continuity objectives, mapping to ISO 22301 and NIST CSF 2.0 Recover. Resilience is a function of how many independent failures must occur before impact a public resource with an over-permissioned role collapses that chain to one. CSPM’s contribution is chain lengthening.
Financial and legal exposure. Cost accrues through incident response, penalties, forensics, notification and often largest delayed revenue when security questionnaires cannot be answered. NIS2 obliges management bodies directly. Documented continuous posture management is a component of a due-care defence.
Trust and supply chain. Enterprise buyers audit supplier posture through questionnaires, SOC 2 Type II reports and evidence requests. CSPM output coverage, exception register, SLA attainment is what mature procurement asks for.
Board reporting. Boards want trend and trajectory: coverage; critical exposures beyond SLA; MTTR trend; open exceptions with expiry and owners.
Digital transformation. Policy-as-code guardrails give engineering deterministic pipeline feedback instead of discretionary review-meeting feedback, moving security from gatekeeper to platform provider.
Technical Deep Dive: How CSPM Reduces Attack Surface Exposure
Modelling attack surface correctly
Cloud attack surface is the set of reachable paths from an untrusted principal to a valuable asset, not a list of assets. This is why finding counts are a poor metric: ten thousand low-severity findings on isolated dev resources matter less than one public endpoint fronting a production database with an over-permissioned instance profile.
| Exposure Class | Representative Misconfiguration | Primary Control Response |
|---|---|---|
| Network | 0.0.0.0/0 on 22/3389/DB ports; public DB endpoints | Private endpoints, SG baselines, egress control |
| Identity | Wildcard actions, unconstrained trust, long-lived keys | Least privilege, permission boundaries, SCPs, CIEM |
| Data | Public object storage, unencrypted or shared snapshots | CMK encryption, block-public-access, DSPM classification |
| Control plane | Public Kubernetes API, no MFA, disabled audit logging | Conditional access, private endpoints, immutable logs |
| Supply chain | Unsigned images, over-privileged runners, secrets in code | Image signing, OIDC short-lived CI credentials, secret scanning |
CSPM addresses the configuration determinants of all five, but does not replace runtime workload protection, vulnerability management or application security testing.
Reference architecture
Six layers: collection (agentless API enumeration plus audit event streams); normalisation (a canonical schema, so “public storage” means the same across S3, Blob and GCS); graph and context (which identity reaches which resource, which subnet routes to the internet, which asset holds classified data); policy evaluation; risk and workflow (scoring, ownership, ticketing, SLA, exceptions); assurance (framework mapping, evidence, dashboards).
Diagram 2 CSPM Reference Architecture
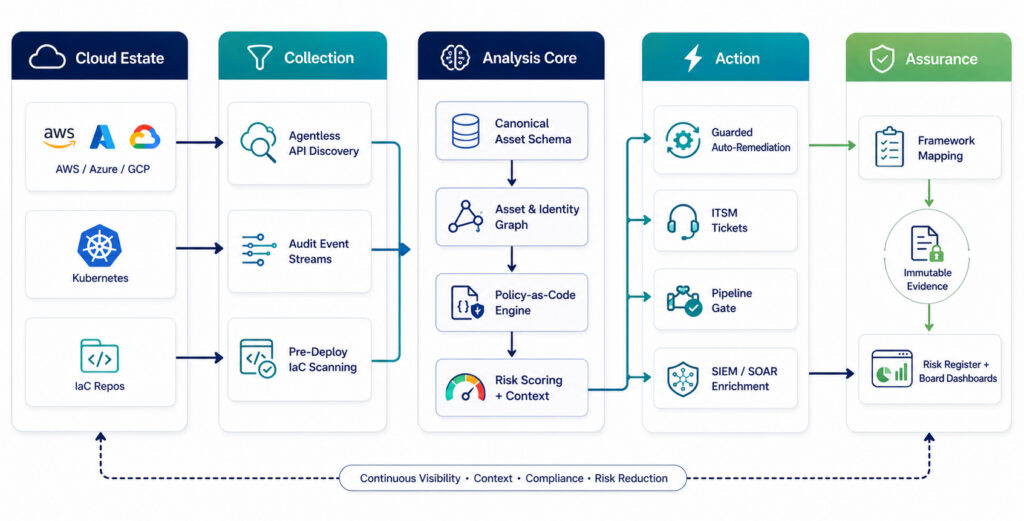
Why it matters: the graph layer separates a compliance scanner from an exposure-reduction platform; without it, prioritisation is guesswork.
Diagram 3 Continuous Posture Lifecycle
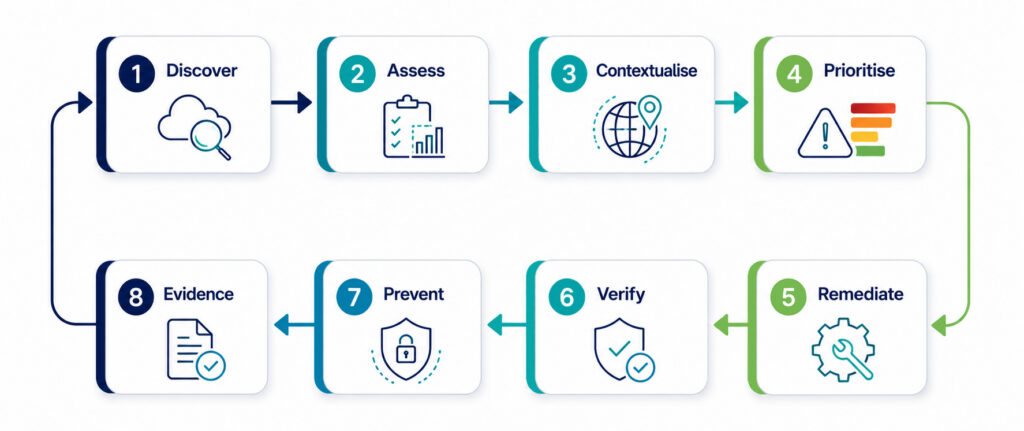
Why it matters: stage 7 is most often omitted, so the same defect class is remediated indefinitely and MTTR never improves.
Evaluation mechanics and policy as code
Three modes run concurrently: periodic full sweep (authoritative for coverage), event-driven evaluation (control-plane events such as PutBucketPolicy triggering assessment in seconds), and pre-deployment scanning of IaC and manifests in pull requests.
package cspm.network
deny[msg] {
sg := input.resource.aws_security_group[name]
rule := sg.ingress[_]
rule.cidr_blocks[_] == “0.0.0.0/0”
rule.from_port <= 22; rule.to_port >= 22
msg := sprintf(“SG ‘%s’ permits unrestricted SSH (control NET-001)”, [name])
}
Preventive guardrails remove an exposure class rather than detecting instances of it:
{ “Sid”: “DenyDisablingCloudTrail”, “Effect”: “Deny”,
“Action”: [“cloudtrail:StopLogging”, “cloudtrail:DeleteTrail”], “Resource”: “*”,
“Condition”: { “ArnNotLike”: { “aws:PrincipalARN”: “arn:aws:iam::*:role/BreakGlass” } } }
Findings should reach the SIEM as enrichment, not alerts. A public bucket is posture; anonymous GetObject calls against it are detection. Value comes from the join UEBA and hunting queries weighting access higher when the target is known-exposed and holds regulated data.
Diagram 4 Attack Path from Misconfiguration to Exfiltration
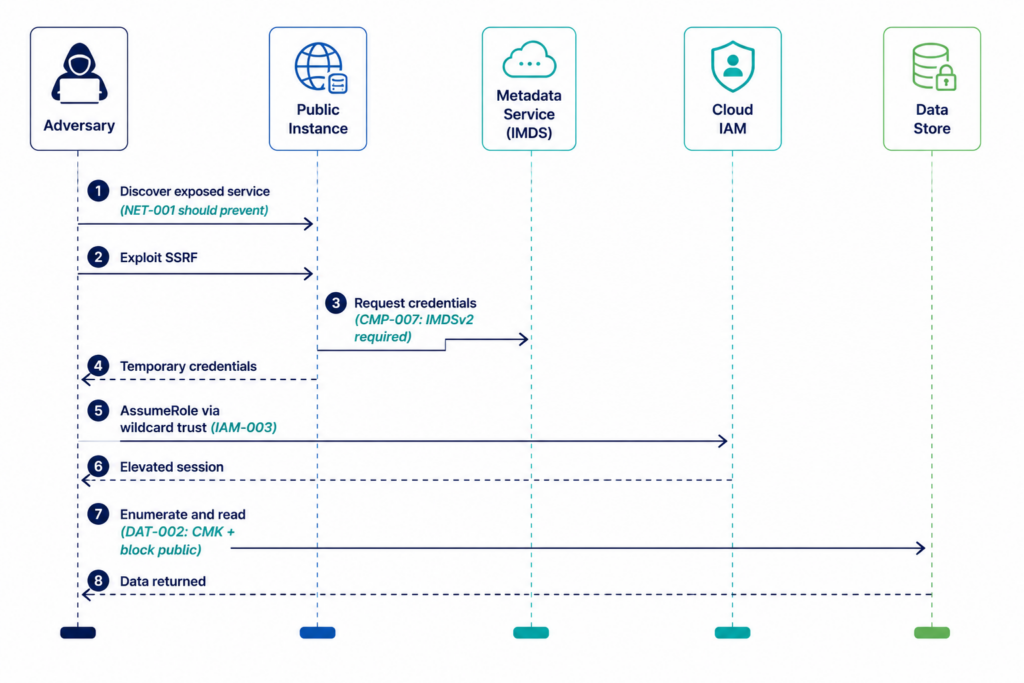
Why it matters: each named control severs the chain. Framing findings as chain-breaking opportunities lands better with engineering, and shows why identity controls often outperform network controls per unit of effort.
Prioritisation and remediation
Effective Risk = Exposure × Identity Blast Radius × Data Sensitivity × Environment Criticality. Vendor severity labels capture none of these.
Diagram 5 Remediation Decision Tree
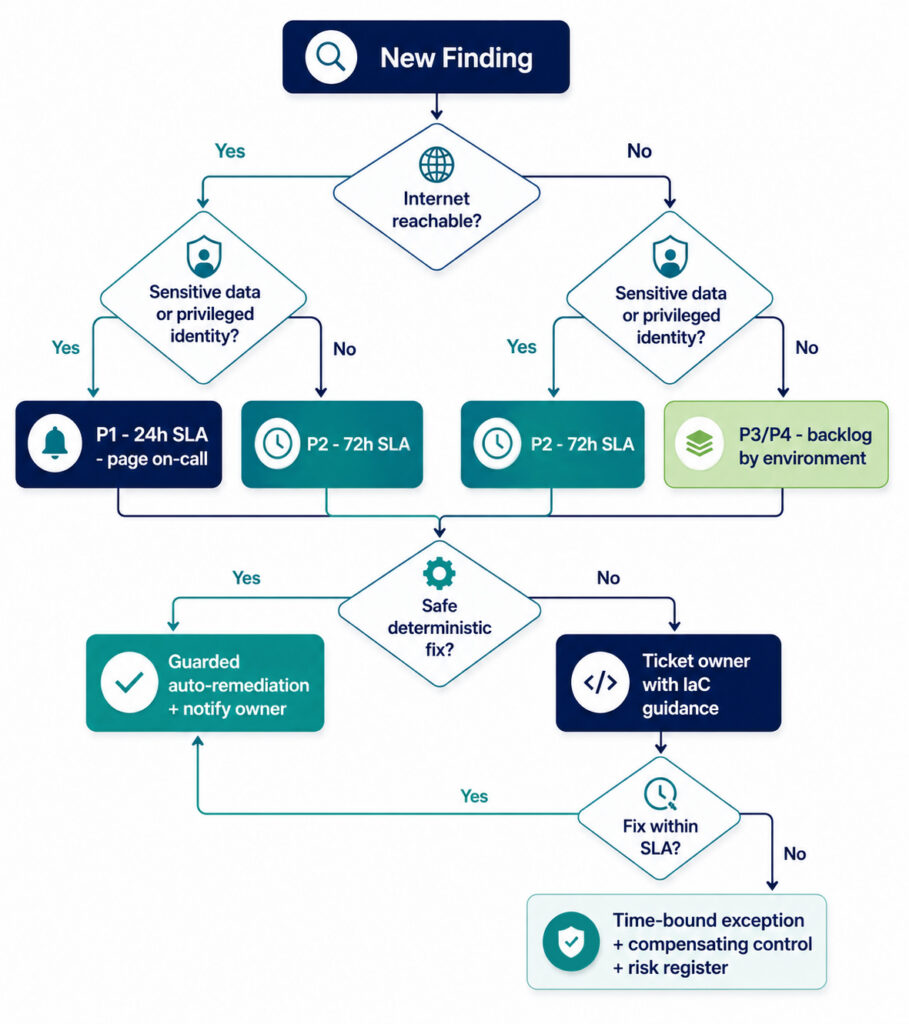
Why it matters: it encodes prioritisation as an auditable artefact, so “why was this open 45 days?” has a documented answer.
| Remediation Mode | Best For | Principal Risk |
|---|---|---|
| Manual ticketing | Complex, context-dependent findings | Slow; regresses if fixed outside IaC |
| Guarded auto-remediation | Deterministic, low-blast-radius controls | Breaks intended config if allowlists are wrong |
| Preventive guardrail | Entire exposure classes | Needs maturity and break-glass design |
Auto-remediation is production code: change-controlled, dry-run tested, scoped by tier, reversible, logged, allowlist-aware, with a documented break-glass path.
Diagram 6 Exception and Risk Acceptance Workflow
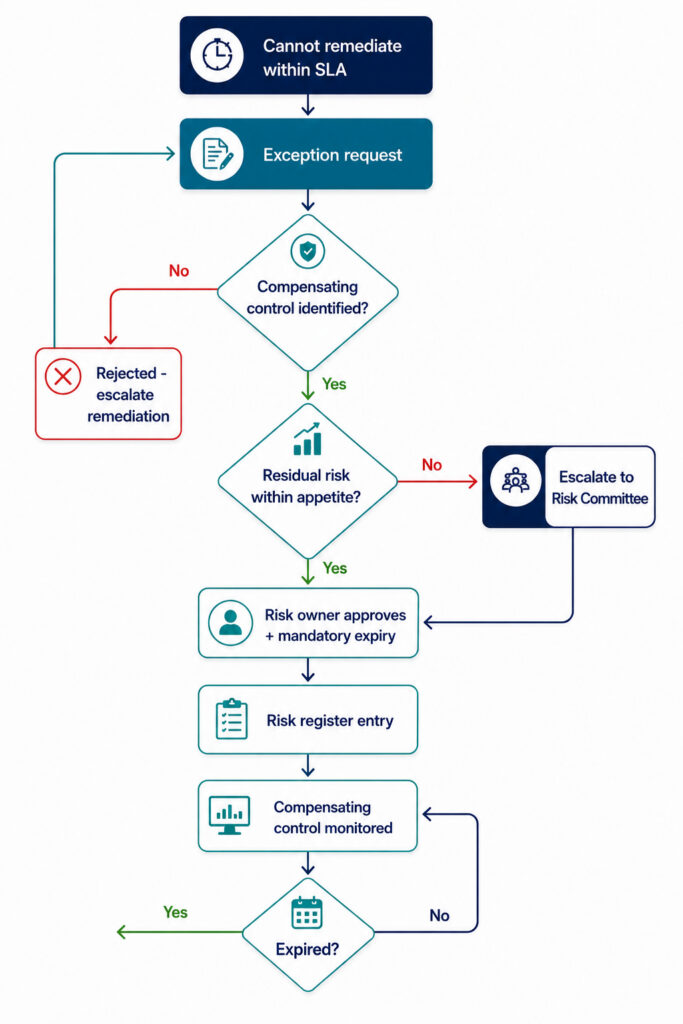
Why it matters: unexpiring exceptions accumulate undeclared risk. Enforced expiry and a named owner satisfy ISO/IEC 27001 Clause 6.1 and 8.3.
Diagram 7 Ownership Swimlane, Detection to Closure
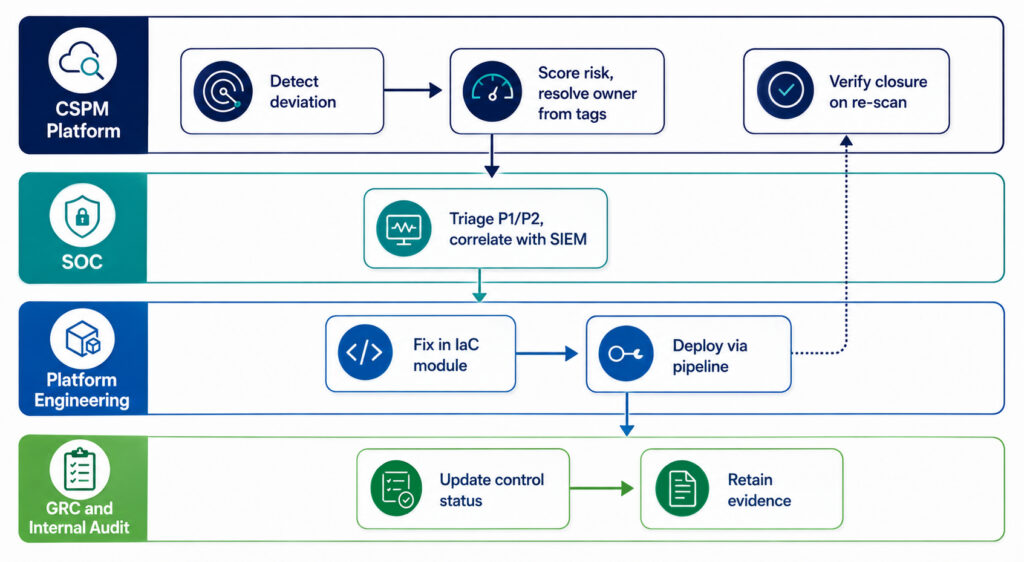
Why it matters: the most common CSPM failure is organisational security owns the tool, engineering owns the fix, and no shared SLA connects them.
| Activity | CISO | Cloud Security | Platform Eng | SOC | GRC |
|---|---|---|---|---|---|
| Define control baseline | A | R | C | C | C |
| Triage critical findings | I | C | C | R/A | I |
| Remediate in IaC | I | C | R/A | I | I |
| Approve exceptions | C | R | C | I | A |
| Evidence and audit response | I | C | I | I | R/A |
Cloud, hybrid, scale and Zero Trust
Provider asymmetry. Equivalent controls have non-equivalent implementations S3 Block Public Access, Azure allowBlobPublicAccess, GCP Public Access Prevention. Canonical definitions with per-provider implementations are essential, or multi-cloud reporting is fiction.
Hybrid and OT. Cloud-native CSPM will not cover on-premises estate; extend the control taxonomy across hybrid even where tooling differs. Where OT is in scope, IEC 62443 zone-and-conduit modelling governs segmentation.
Kubernetes (KSPM). RBAC over-permissioning, privileged pods, host-path mounts, absent network policies and public API servers must be evaluated at IaC, admission control and running state.
Scale. Large estates hit API rate limits. Use bulk inventory services (AWS Config aggregators, Azure Resource Graph, GCP Cloud Asset Inventory) rather than per-resource calls.
Trade-offs. Scan frequency trades detection latency against cost; broad auto-remediation trades MTTR against change risk; aggressive guardrails trade exposure against engineering friction. These are governance decisions with named owners, not technical defaults.
Zero Trust. Against NIST SP 800-207 tenets, CSPM verifies explicitly, enforces least privilege (with CIEM measuring granted versus used entitlement), and supports assume-breach through segmentation, encryption and logging. Zero Trust fails when architecture is designed but never verified in production; CSPM is that verification layer.
Metrics and maturity
| Metric | Type | Definition |
|---|---|---|
| Inventory coverage | KPI | % of accounts onboarded to CSPM |
| Critical exposure count | KRI | Open P1 findings (internet-reachable and sensitive) |
| MTTR (critical) | KPI | Median hours, detection to verified closure |
| SLA attainment | KPI | % closed within severity SLA |
| Preventive coverage | KPI | % of controls enforced preventively vs detectively |
| Recurrence rate | KRI | % of closed findings reappearing within 30 days |
| Drift rate | KRI | Config changes made outside the IaC pipeline |
Recurrence and drift are the most diagnostic: both reveal whether causes or symptoms are being fixed.
Diagram 8 Maturity Progression
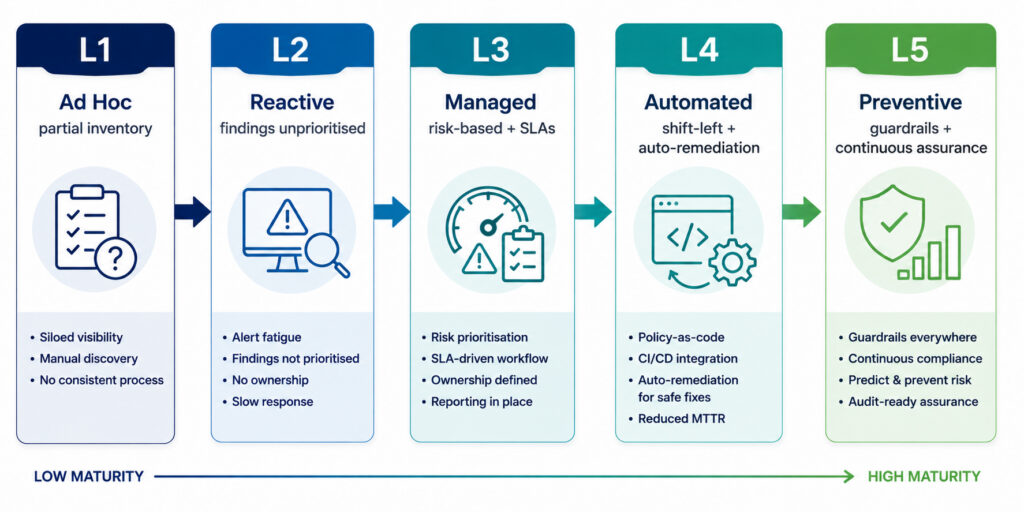
Why it matters: most enterprises plateau at Level 2. Progression to Level 3 is organisational ownership, SLAs, tagging not technical.
Framework Mapping
One CSPM control evaluation produces evidence across multiple frameworks. Validate exact identifiers against the current published version of each standard, since numbering changes between revisions notably ISO/IEC 27001:2022’s restructured Annex A and NIST CSF 2.0’s added Govern function.
| CSPM Control Domain | ISO 27001:2022 | NIST CSF 2.0 | SP 800-53 r5 | CIS v8 | CSA CCM | SOC 2 | PCI DSS v4.0 |
|---|---|---|---|---|---|---|---|
| Asset inventory | A.5.9 | ID.AM | CM-8 | 1, 2 | DCS | CC3.2 | Req. 2, 12 |
| Secure baselines | A.8.9 | PR.PS | CM-2, CM-6 | 4 | IVS | CC7.1 | Req. 2 |
| Network exposure | A.8.20, A.8.22 | PR.IR | SC-7 | 12, 13 | IVS | CC6.6 | Req. 1 |
| Identity and access | A.5.15, A.5.18 | PR.AA | AC-2, AC-3, AC-6 | 5, 6 | IAM | CC6.1-6.3 | Req. 7, 8 |
| Logging and monitoring | A.8.15, A.8.16 | DE.CM, DE.AE | AU-2, AU-6, AU-12 | 8 | LOG | CC7.2 | Req. 10 |
| Governance and risk | A.5.1-A.5.4 | GV.OC, GV.RM | PM-9, RA-3 | 14, 17 | GRC | CC1.x | Req. 12.1 |
Privacy and sectoral. GDPR Art. 32 and Art. 25 are supported by continuous verification and secure-by-default provisioning; ISO/IEC 27701 extends this to a PIMS. The DPDP Act 2023, CCPA/CPRA and HIPAA §164.312 map to the same checks on personal-data and ePHI-bearing services. NIS2 adds management-body accountability; ISO 22301 and COBIT govern the continuity and governance wrappers.
| ATT&CK Technique | Preventive Control | Detective Signal |
|---|---|---|
| T1190 Exploit Public-Facing App | Restrict ingress; require WAF | New public exposure event |
| T1078.004 Valid Cloud Accounts | Prohibit static keys; enforce MFA | Impossible travel, anomalous region (UEBA) |
| T1530 Data from Cloud Storage | Block public access; CMK encryption | Anonymous GetObject volume |
| T1562.008 Disable Cloud Logs | SCP denying StopLogging | Logging-config change alert |
| T1537 Transfer Data to Cloud Account | Deny sharing to non-allowlisted accounts | Resource-sharing config change |
CSPM maps principally to MITRE D3FEND‘s Harden tactic and enriches Detect with authoritative asset context. OWASP guidance governs the application layer above CSPM’s scope.
Enterprise Checklists
CISO. One accountable executive for posture, separate from cost ownership · exposure appetite quantified and approved · SLAs agreed jointly with engineering · exception authority and expiry limits in policy · posture in the enterprise risk register · supplier posture assessed within TPRM · budget covers the operating model, not only the licence.
Architecture review. All accounts onboarded · landing zone secure-by-default for networking, logging and encryption · guardrails deny high-risk actions · private connectivity default for data services · workload identity federation replaces static credentials · break-glass accounts MFA-protected and tested · immutable central log destination · customer-managed keys for regulated data · tagging enforced at provisioning.
SOC. Findings ingested as asset enrichment, not raw alerts · detections weighted by exposure and data classification · P1 posture events page on-call · playbooks for the top posture incident types · SOAR containment tested quarterly · hunting hypotheses drawn from the exposure graph.
Compliance and audit. Control catalogue mapped to all in-scope frameworks · every control has owner, test method, frequency and evidence artefact · evidence automated, time-stamped, immutably stored · exception register complete with approvers and expiry · internal audit re-performs a control sample each cycle.
Incident response. Capture configuration state before changing it · preserve both log planes · determine whether access occurred · contain by removing exposure and revoking sessions and keys · assess identity blast radius · engage DPO and legal early for regulated data · root-cause at IaC level · convert the cause into a guardrail and a detection rule.
Enterprise Example
Composite illustration for instructional purposes; not an actual organisation or event.
Organisation. A multinational financial services group, 9,000 staff across the UK, EU and India, subject to PCI DSS, GDPR and the DPDP Act, ISO 27001 certified. 214 AWS accounts plus 38 Azure subscriptions from a 2023 acquisition; Terraform standard, though the acquired estate is ~40% console-managed. CSPM deployed 14 months prior covering AWS only.
Threat and detection. A team enabled a public endpoint on an Azure Storage account via the portal, not IaC. It held tokenised card data and an export of 42,000 customer records. Because the acquired subscriptions were never onboarded, the exposure was invisible for 19 days; detection came from an external threat-intelligence notification.
Investigation and risk. Data-plane logging was not enabled a second control failure. Control-plane logs established when and by whom access was enabled, but not whether objects were read. Residual risk was assessed Critical, driven by forensic uncertainty.
Root cause. Inventory gap (integration tracked connectivity, not posture); process gap (no guardrail against portal changes in production); telemetry gap (an AWS-shaped catalogue never required data-plane logging on Azure).
Impact. GDPR notification within 72 hours plus data-subject communication; DPDP breach intimation assessed; PCI scope revalidation; ISO 27001 nonconformity against A.5.9 and A.8.15 under Clause 10.2; a SOC 2 exception disclosed. Two enterprise deals paused pending security review.
Remediation. Access removed, keys rotated, data-plane logging enabled, all 38 subscriptions onboarded surfacing eleven further public endpoints. Azure Policy now denies allowBlobPublicAccess at management-group scope, the catalogue was rewritten cloud-agnostically, and the M&A runbook gates production connectivity on CSPM onboarding.
Lessons. Coverage is a prerequisite for detection; a single-provider catalogue silently fails on a second provider; missing telemetry converts a contained exposure into an assumed breach. The board report carried no finding counts: timeline, forensic confidence, notification position, root causes with owners, and a new coverage KRI for acquired estates.
Common Enterprise Mistakes
| Mistake | Why It Happens | Risk | Correct Approach |
|---|---|---|---|
| CSPM bought as a tool, not an operating model | Budget rewards procurement | Spend without exposure reduction | Fund ownership, tagging, SLAs, capacity |
| Incomplete account onboarding | Decentralised creation and M&A | Unmeasured exposure | Auto-onboard at creation; coverage as a KRI |
| Default policy pack unmodified | Enabling everything feels rigorous | Noise hides critical findings | Tier the baseline; expand deliberately |
| Prioritising by severity label | It is the field the tool provides | Effort misallocated | Score by exposure × identity × data × environment |
| Remediating in the console | Fastest way to close a ticket | Recurrence at next apply | Fix in IaC; measure recurrence |
| Estate-wide auto-remediation on day one | MTTR pressure | One broken service ends the mandate | Phase by tier; dry-run; allowlist; rollback |
| Ignoring identity posture | IAM analysis is specialist work | Highest-impact paths stay open | Integrate CIEM; escalation paths are P1 |
| Exceptions treated as permanent | Nothing forces re-review | Undeclared accumulated risk | Mandatory expiry, named owner, monitored control |
| Untagged, unowned resources | Tagging seen as a FinOps concern | Findings unassignable; orphans persist | Enforce tags at provisioning via policy |
| CSPM isolated from the SOC | Separate procurement and tooling | Exposure and access never correlated | Publish posture to SIEM as enrichment |
| Single-cloud catalogue, multi-cloud estate | Catalogue written for one provider | False assurance | Cloud-agnostic controls, per-provider mappings |
| Kubernetes excluded from scope | Seen as a platform concern | Workloads and secrets ungoverned | KSPM at IaC, admission and runtime |
| Incomplete or mutable audit logging | Cost-visible, benefit invisible | Cannot scope a breach | Both log planes; immutable store; deny disablement |
| Deferring M&A estate onboarding | Integration prioritises connectivity | Immediate inherited liability | Gate connectivity on posture assessment |
Implementation Roadmap
| Phase | Objective | Key Deliverables | Expected Outcome |
|---|---|---|---|
| 1. Foundation (0-3m) | Authoritative inventory and named ownership | Organisation-level integration; auto-onboarding; tagging standard; baseline assessment; RACI | Evidence-based answer to what we own and what is exposed; no SLA enforcement yet, by design |
| 2. Baseline (3-6m) | Governed, risk-ranked workload | Cloud-agnostic catalogue mapped to frameworks; tiered enforcement; contextual scoring; SLAs in ITSM; exception process | Owner-assigned backlog; first reliable MTTR baseline |
| 3. Remediation (6-12m) | Reduce exposure faster than it is created | IaC scanning in pull requests; blocking gates; phased auto-remediation; secure-by-default modules; drift reporting | Falling MTTR and recurrence; less new exposure in production |
| 4. Prevention (12-18m) | Eliminate exposure classes; integrate detection | SCPs, Azure Policy, admission control; SIEM enrichment; SOAR playbooks; CIEM and DSPM integration; tested break-glass | Preventive coverage becomes a KPI; misconfiguration classes stop recurring |
| 5. Assurance (18m+) | Audit-grade assurance and board narrative | Continuous Controls Monitoring; auditor-consumable evidence; risk-register integration; KRI reporting; annual catalogue review | Reduced audit effort; exposure within approved appetite |
Best Practices
- Appoint one accountable executive for posture, separate from cost ownership.
- Automate onboarding at account, subscription and project creation.
- Report inventory coverage before any finding metric.
- Build a cloud-agnostic control catalogue with per-provider implementations.
- Map controls to frameworks once; generate all reporting from that mapping.
- Enforce owner, environment, data-classification and business-service tags at provisioning.
- Tier the baseline: critical controls estate-wide, extended controls in production.
- Score risk by exposure, identity blast radius, data sensitivity and environment.
- Agree SLAs jointly with engineering rather than imposing them.
- Require remediation at the IaC source of truth.
- Measure recurrence rate as the programme’s honesty metric.
- Convert every recurring finding class into a preventive guardrail.
- Phase auto-remediation by tier with dry-run, allowlists and rollback.
- Treat auto-remediation logic as production code under change control.
- Prohibit static credentials; use workload identity federation and OIDC.
- Integrate CIEM to close the gap between granted and used entitlements.
- Integrate DSPM so data sensitivity is an input, not an assumption.
- Centralise logs immutably and deny disablement by policy.
- Publish findings into the SIEM as enrichment, not alerts.
- Evaluate Kubernetes posture at IaC, admission control and runtime.
- Scan IaC in pull requests with developer-facing remediation guidance.
- Publish secure-by-default IaC modules so the easy path is the compliant path.
- Enforce expiry, a named risk owner and a compensating control on every exception.
- Gate M&A production connectivity on posture onboarding.
- Review the control catalogue annually against threat intelligence and framework revisions.
How ServQual and SUSAN Help
CSPM output becomes enterprise risk management only when connected to a governance layer maintaining the control catalogue, risk register, evidence trail and accountability model. This is where ServQual (SRQL) and its platform SUSAN are positioned at the junction between cloud technical posture and enterprise GRC.
Continuous GRC and control monitoring. CSPM produces a high-frequency stream of control outcomes; a continuous GRC layer converts these into control status, trend and assurance rather than a findings queue. ServQual is positioned in continuous monitoring of controls across security, privacy and risk.
Compliance and control mapping. The many-to-one mapping described above requires a maintained catalogue with framework crosswalks where SUSAN is intended to support compliance and control mapping.
Risk register and asset inventory. Exposures not remediable within SLA must become governed risk entries with owners, treatment plans and review dates. Prioritisation depends on business context service, data classification, ownership. ServQual is positioned in risk management, asset inventory, and security assessments and continuous assurance, so manual and automated results reconcile against one catalogue.
Evidence, workflow and dashboards. Auditors require time-stamped, traceable evidence; remediation routing, exception approval and escalation are workflow problems. ServQual is positioned in evidence management, workflow automation, incident management and governance dashboards, and across cybersecurity and privacy where personal data is exposed.
Scope note. Actual capabilities, integrations and coverage depend on deployment scope, licensing and organisational requirements. Confirm specific functionality directly with ServQual as part of your own due diligence. Nothing here states a guaranteed capability, certification or outcome.
| Function | CSPM/CNAPP Tooling | GRC Layer |
|---|---|---|
| Discovery and configuration evaluation | ✔ | - |
| Attack path and entitlement analysis | ✔ | - |
| Control catalogue and framework crosswalks | - | ✔ |
| Risk register, treatment, risk acceptance | - | ✔ |
| Exception governance with expiry | Partial | ✔ |
| Evidence retention and audit packaging | Partial | ✔ |
Buying only the left column yields detection with no governance narrative; only the right yields a catalogue with no live data behind it.
"CSPM is not a dashboard. It is a governance loop for reducing cloud exposure."
Harshal Patil
Director of Accounts | ServQual
FAQ
Most frequent questions and answers
CSPM, or Cloud Security Posture Management, is the continuous discovery of cloud resources, evaluation of cloud configuration against security baselines, and remediation of deviations before they become exploitable.
CSPM reduces cloud attack surface by identifying exposed resources, public storage, unrestricted network rules, over-permissioned identities, weak logging, encryption gaps and control-plane exposure, then routing those issues to remediation.
No. Vulnerability management focuses on software flaws and missing patches. CSPM focuses on cloud configuration risk, cloud misconfiguration, identity exposure, public access and control drift.
CSPM is one layer of cloud security focused on posture and configuration. CNAPP is broader and may combine CSPM, CWPP, CIEM, KSPM, DSPM and attack path analysis into a unified cloud-native security platform.
Common CSPM findings include public object storage, unrestricted inbound rules, wildcard IAM permissions, long-lived access keys, disabled audit logging, unencrypted storage, missing MFA and public Kubernetes API endpoints.
CSPM findings should be prioritized by reachability, identity blast radius, data sensitivity, environment criticality, business impact and remediation status instead of relying only on vendor severity labels.
CSPM supports compliance by continuously testing cloud controls, preserving evidence, tracking remediation, validating secure configuration and mapping control outcomes to frameworks such as ISO 27001, SOC 2, PCI DSS, NIST CSF, GDPR and DPDP.
CSPM supports Zero Trust by verifying that least privilege, segmentation, encryption, logging, private access and control-plane protections are actually configured in production environments.
CSPM programmes often fail when they are treated as tools instead of operating models. Common causes include incomplete cloud onboarding, no asset ownership, no remediation SLAs, excessive findings, console-level fixes and weak integration with GRC workflows.
SUSAN can help connect CSPM findings with control mapping, risk register entries, remediation ownership, exception governance, evidence management, dashboards and Continuous Assurance workflows.
Reduce Cloud Attack Surface with Continuous CSPM Governance
Cloud misconfiguration can expose regulated data, privileged identities and critical systems faster than periodic reviews can detect. CSPM helps organizations continuously discover assets, detect exposure, prioritize remediation and maintain audit-ready evidence.
ServQual helps enterprises strengthen cloud security posture, cloud governance, risk management and compliance readiness across AWS, Azure, Google Cloud, Kubernetes and Microsoft 365 environments.
Explore SUSAN or contact ServQual to connect CSPM findings, control mapping, remediation ownership, exception governance and Continuous Assurance into one structured GRC view.