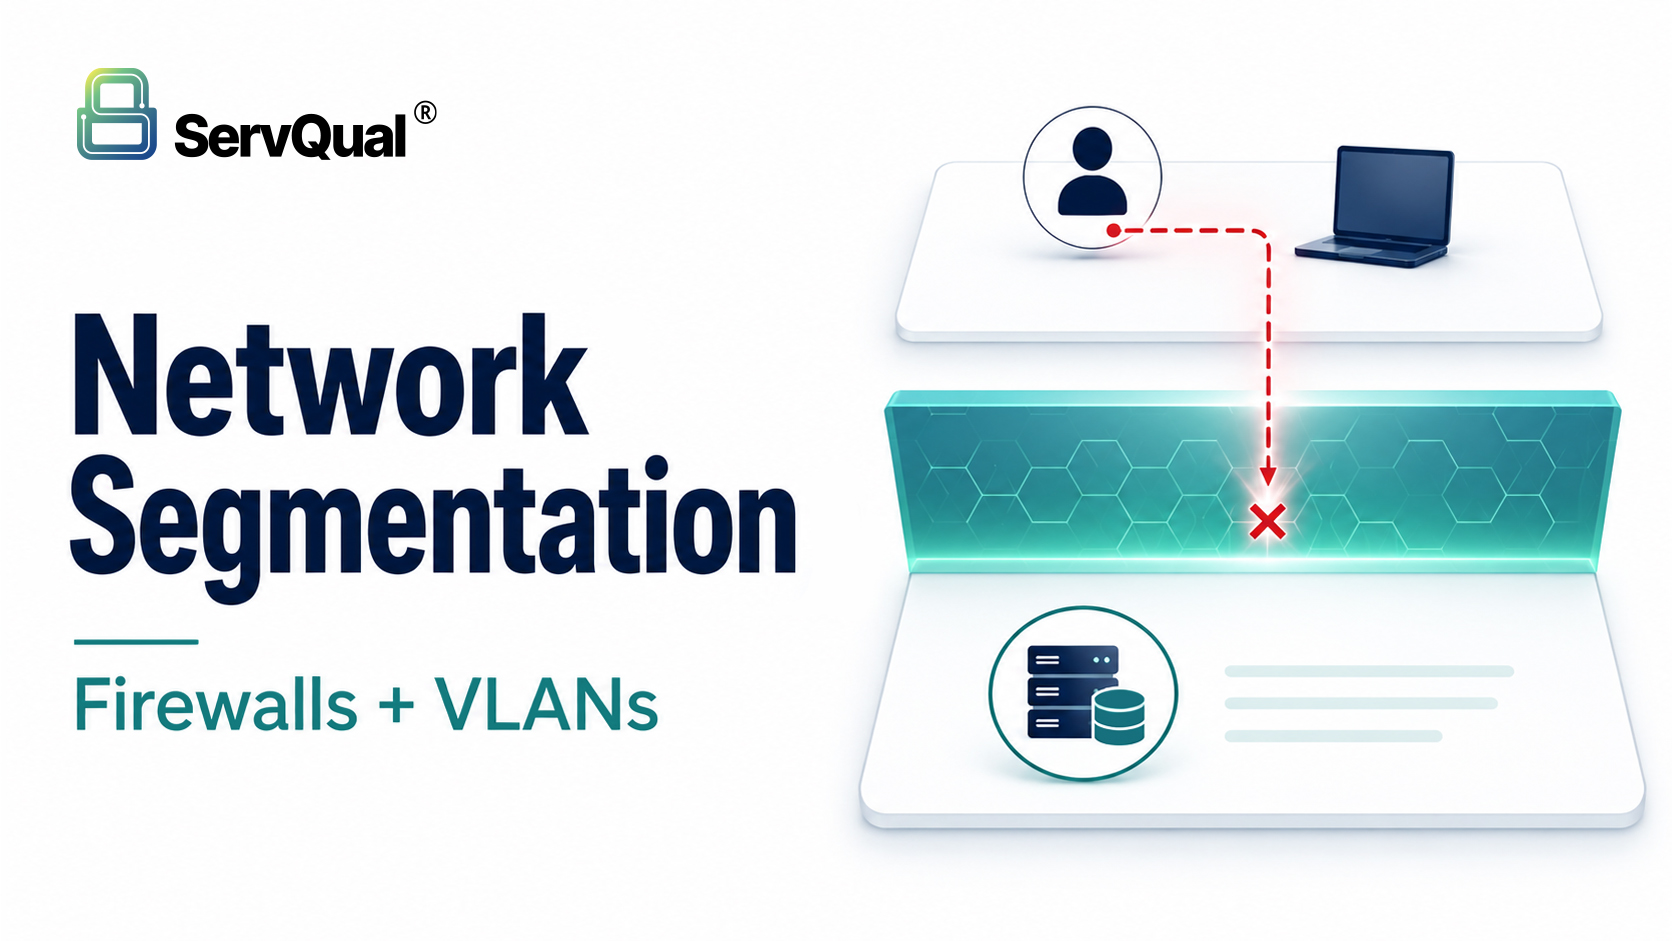
Network segmentation with firewalls and VLANs reduces lateral movement by dividing the network into smaller zones and controlling which traffic can pass between them. VLANs create logical network segments, while firewalls enforce access policy between those segments.
A strong segmentation design separates users, servers, databases, management systems, IoT devices, printers, guest wireless, backups and DMZ services. It should use default deny rules, allow only required traffic, log inter-zone access, monitor east-west movement and regularly review firewall rules and VLAN objects.
Executive Summary
A flat network is easy to build but difficult to defend. When every device can reach every other device, one compromised workstation can become a path to file servers, domain controllers, databases and backup systems.
Network segmentation limits that damage. VLANs group devices into logical zones, and firewalls decide what traffic is allowed between those zones. Together, they reduce lateral movement, improve visibility, limit ransomware spread and help organizations manage compliance scope.
Segmentation is especially important for sensitive zones such as management networks, backup networks, database servers, IoT devices, guest wireless and DMZ services. These zones should not communicate freely. Each connection should have a business purpose, defined rule, owner and log trail.
This article explains how VLANs and firewalls work together, why segmentation matters, how micro-segmentation strengthens east-west control and what teams should monitor to keep segmentation effective over time.
Why Network Segmentation Matters
Network segmentation is the practice of dividing a single network into smaller, isolated sections so that traffic between them can be controlled. Instead of allowing every device to reach every other device, each section is treated as a separate zone with its own access rules.
A flat network, where all servers, workstations, printers and other devices share the same broadcast domain, is convenient to build but difficult to defend. Once an attacker gains a foothold on any single host, nothing stops them from reaching the rest. A malware infection on one laptop can talk directly to file servers, domain controllers and databases because the network never questions internal traffic.
Segmentation changes that. By grouping devices into zones and controlling what may pass between them, a single point of entry becomes a contained event rather than a full compromise. This limits data loss, slows attackers, reduces ransomware spread and shrinks the scope of compliance and audit.
Flat Network vs Segmented Network
| Aspect | Flat Network | Segmented Network |
|---|---|---|
| Internal traffic | Any host reaches any host | Controlled by policy |
| Breach impact | Spreads network wide | Contained to one zone |
| Visibility | Limited, mostly perimeter | Inspected between zones |
| Compliance scope | Entire network in scope | Reduced to relevant zones |
| Troubleshooting | Broad broadcast noise | Isolated, predictable |
Understanding Lateral Movement
Lateral movement describes the steps an attacker takes to expand access after the initial breach. A typical path begins with a phishing email or an exposed service. Once one workstation is under control, the attacker harvests cached credentials, scans nearby subnets, and connects to any reachable system using stolen accounts or unpatched vulnerabilities.
Internal systems are the real target because that is where value sits: financial records, customer databases, intellectual property and backup servers. Perimeter defenses do little once the attacker is already inside. When internal communication is unrestricted, a compromise of a low value device such as a reception PC can lead directly to domain controllers and production databases. The business impact includes data theft, ransomware encryption across shared systems, extended downtime and regulatory penalties.
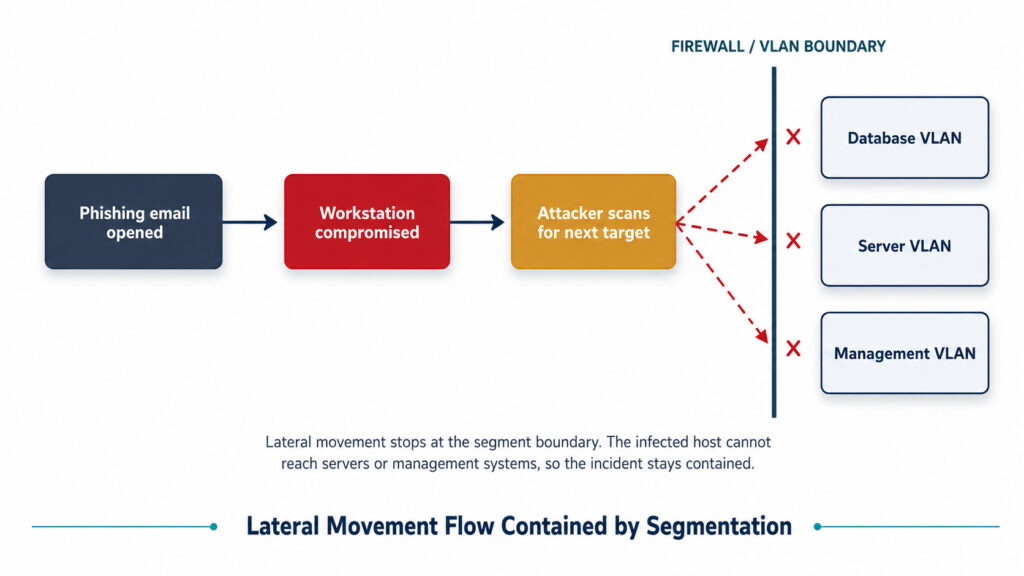
Figure 1: How segmentation stops lateral movement at the zone boundary.
What Is VLAN Segmentation?
A VLAN (Virtual Local Area Network) is a logical grouping of devices on a switch that behaves as a separate network, even when devices share the same physical hardware. Each VLAN is its own broadcast domain, so broadcast traffic and Layer 2 discovery stay within that VLAN and do not leak into others.
Separating device types into different VLANs limits who can talk to whom and reduces the reach of any single compromise. Common VLANs in an enterprise and the reason each is isolated:
- User VLAN: standard employee workstations, kept away from servers and infrastructure.
- Voice VLAN: IP phones, separated for call quality and to avoid mixing with data traffic.
- Server VLAN: application and database servers, restricted to required client ports only.
- Management VLAN: switch, firewall and hypervisor administration, isolated so control planes are unreachable from user space.
- Guest VLAN: visitor devices with internet only access and no path to internal resources.
- IoT VLAN: sensors and smart devices that are rarely patched and should never reach core systems.
- Printer VLAN: print devices confined to print and scan services.
- Access VLAN: the VLAN assigned to a specific switch port for an end device.
- DMZ VLAN: internet facing services such as web and mail relays, kept apart from the internal network.
VLAN Segmentation vs Firewall Segmentation
| Factor | VLAN Segmentation | Firewall Segmentation |
|---|---|---|
| Layer | Layer 2 separation | Layer 3 to Layer 7 control |
| Purpose | Isolate broadcast domains | Enforce security policy |
| Traffic inspection | None by itself | Stateful, deep inspection |
| Logging | Minimal | Detailed allow and deny logs |
| Best role | Group devices logically | Decide what may cross zones |
VLANs and firewalls work together. VLANs create the zones; firewalls decide what traffic is allowed between them. A VLAN alone does not stop routed traffic between subnets, so a control point is still needed.
Role of Firewalls in Network Segmentation
The firewall is the policy enforcement point that sits between VLANs and inspects traffic crossing zone boundaries. Its role in a segmented design is to:
- Control communication between VLANs and permit only defined flows.
- Apply security policies based on source, destination and service.
- Restrict unnecessary traffic and block ports and protocols that are not required.
- Filter applications and identify traffic beyond port numbers.
- Perform user or group-based access control tied to directory identity.
- Log both permitted and denied traffic for investigation and auditing.
Reduce the attack surface by exposing each zone only to the services it genuinely needs.
Layer 2 vs Layer 3 Segmentation
Segmentation can be enforced at different points, and each has a suitable role.
| Method | How It Works | When to Use |
|---|---|---|
| Switch VLANs (L2) | Groups ports into broadcast domains | Baseline device grouping |
| Router / L3 switch | Routes and filters with ACLs | High speed internal routing |
| Firewall | Stateful inspection and policy | Sensitive zone boundaries |
Switch VLANs group devices but do not inspect traffic. Router or Layer 3 switch ACLs provide fast basic filtering for high throughput internal segments. Firewalls give the deepest control and logging and belong at the boundaries of sensitive zones such as servers, databases and management.
Micro-Segmentation for East-West Traffic
Traditional segmentation groups many systems into a handful of large zones. Micro-segmentation goes further and applies policy around individual workloads or servers, even within the same VLAN.
This controls server to server, or east-west, traffic. For example, a web server may be allowed to reach only its application server on one port, and the application server may reach only its database on the database port. If one server is compromised, it cannot pivot to unrelated servers sitting beside it. This workload isolation is important because most internal traffic never crosses the perimeter firewall and would otherwise go uninspected.
Recommended Enterprise Network Segmentation
A practical enterprise layout separates traffic into dedicated networks, each with its own policy. The architecture below shows this arrangement, which typically includes:
Internet, perimeter firewall, DMZ, VPN users, server network, application servers, database servers, user LAN, voice network, corporate wireless, guest wireless, printers, CCTV, IoT devices, management network and backup network.
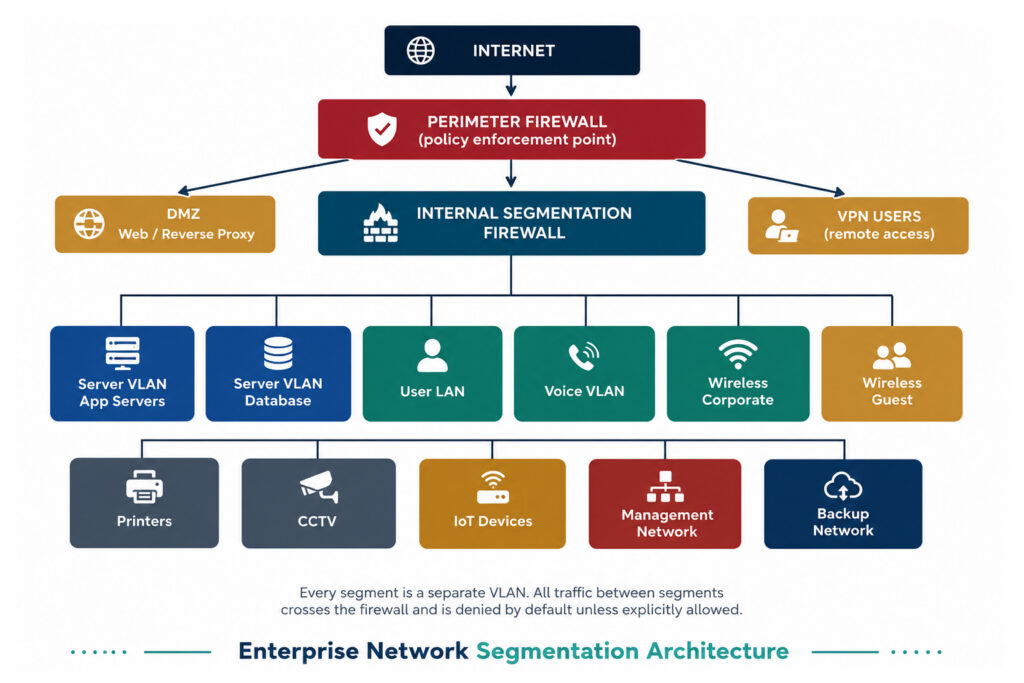
Figure 2: Example enterprise segmentation architecture.
These networks should not communicate freely because their trust levels differ. Guest wireless and IoT devices are low trust and must never reach servers or management. Databases should accept connections only from their application servers, not from user workstations. The management and backup networks hold the keys to recovery and are the most sensitive, so they are the most tightly restricted.
Inter-VLAN Traffic Control
Inter-VLAN policy should follow a default deny approach: block everything, then allow only the services each zone requires. Common permitted flows include DNS, DHCP and NTP to infrastructure servers, Active Directory authentication for domain members, file and email access where needed, and specific application to database ports.
| Traffic | Example | Decision |
|---|---|---|
| User to AD / DNS | Workstation to domain controller (53, 88, 389) | Allow |
| App to database | App server to DB on 1433 / 3306 | Allow |
| User to database | Workstation directly to database | Block |
| Guest to internal | Guest Wi-Fi to file server | Block |
| IoT to management | Camera to switch management | Block |
Network Segmentation Best Practices
A segmented network stays effective only with disciplined configuration and upkeep:
- Apply least privilege and Zero Trust: trust no traffic by default and verify every flow.
- Keep a separate management network and require multi-factor authentication for administrators.
- Restrict administrative access to specific hosts and accounts.
- Disable unused switch ports and enable Port Security to limit MAC addresses per port.
- Enable DHCP Snooping, Dynamic ARP Inspection and IP Source Guard to stop spoofing at Layer 2.
- Use Private VLANs where clients should not talk to each other, and apply ACLs where appropriate.
- Log all security events, review firewall rules regularly, and remove unused VLANs and objects.
Run periodic audits, keep network documentation current, and back up firewall and switch configurations.
Monitoring and Visibility
Segmentation reduces risk, but only monitoring confirms the rules are holding. Continuous visibility should cover inter-VLAN traffic, firewall logs, authentication logs and failed login attempts. Watching east-west traffic and internal scanning helps detect suspicious lateral movement early, since a workstation suddenly probing server ports is a strong indicator of compromise. Policy violations and traffic anomalies feed into a central log or SIEM for correlation and alerting.
Common Segmentation Mistakes
- Any to any allow rules that quietly defeat the whole design.
- Poor VLAN design and a shared management VLAN mixed with user traffic.
- No DMZ separation, leaving internet facing services next to internal systems.
- Excessive firewall rules and unused objects that hide risky permissions.
- A flat server network where every server can reach every other server.
- No logging, missing documentation, and no periodic rule cleanup.
Practical Example: Ransomware Contained by Segmentation
A manufacturing company separated its network into user, finance, server, database and management VLANs, with a firewall enforcing default deny between them. An employee in the finance department opened a malicious attachment, and ransomware began encrypting local files and scanning for network shares.
The malware attempted to reach file servers and database servers in other VLANs. Because the firewall only permitted finance workstations to reach the specific application services they needed, every attempt to connect to the server and database VLANs was denied and logged. The infection was confined to the finance user VLAN. Servers, backups and other departments continued operating, and recovery was limited to reimaging a small number of workstations rather than rebuilding the entire environment.
Network Segmentation Checklist
Organizations reviewing network segmentation should validate these controls:
- Identify critical assets, user groups, servers, databases, backups, management systems, IoT devices, printers and guest networks.
- Separate devices into VLANs based on role, trust level and business function.
- Use firewalls as enforcement points between sensitive zones.
- Apply default deny between VLANs and allow only required services.
- Block direct user workstation access to database and management networks.
- Isolate guest wireless and IoT devices from internal systems.
- Keep management networks separate from user and server traffic.
- Restrict backup networks to approved systems and administrators.
- Use micro-segmentation for sensitive server-to-server communication.
- Harden Layer 2 controls with Port Security, DHCP Snooping, Dynamic ARP Inspection and IP Source Guard.
- Log allowed and denied inter-zone traffic.
- Monitor east-west traffic for scanning, unusual access and lateral movement.
- Review firewall rules, VLANs and unused objects regularly.
- Maintain current network diagrams, rule ownership and change records.
- Test segmentation during tabletop exercises, red team activities or ransomware readiness reviews.
How ServQual and SUSAN Help
ServQual helps organizations strengthen network security through firewall architecture review, VLAN segmentation review, secure infrastructure design, incident response, managed security and GRC readiness.
Network segmentation should not be treated as a one-time design project. Business applications change, new VLANs are added, firewall rules expand and temporary exceptions become permanent. Without ongoing review, segmentation can weaken over time.
SUSAN can help teams connect network segmentation findings, remediation ownership, control evidence and audit readiness into a structured governance view. This helps network, security, SOC and GRC teams track whether segmentation risks are identified, assigned, remediated and evidenced.
With ServQual and SUSAN, organizations can
- Review segmentation architecture across VLANs, firewalls and sensitive zones
- Identify flat network exposure and lateral movement paths
- Track remediation for firewall rules, VLAN objects and access paths
- Connect segmentation findings with GRC and compliance workflows
- Support audit-ready evidence for network security reviews
- Improve leadership visibility into internal network risk
- Maintain evidence for change management and review cycles
- Move from static segmentation diagrams to continuous assurance
Explore Cybersecurity Services: https://srql.com/services/cyber-security-solutions/
Explore Incident Response & Managed Security: https://srql.com/services/incident-response-managed-security/
Explore Governance, Risk, Compliance & Audits: https://srql.com/services/governance-risk-compliance-audits/
Explore SUSAN: https://srql.com/services/susan/
"A flat network turns one compromised device into a path across the enterprise."

Rohan Kanthe
Sr. IT Engineer | ServQual
FAQ
Most frequent questions and answers
Network segmentation is the practice of dividing a network into smaller zones so traffic between them can be controlled, monitored and restricted by policy.
VLANs separate devices into logical broadcast domains. They help group users, servers, guests, IoT devices and management systems into separate network zones.
No. A VLAN creates a logical segment, but it does not enforce deep security policy by itself. Firewalls, ACLs, monitoring and Layer 2 controls are needed to enforce and validate segmentation.
Firewall segmentation places a firewall between network zones so traffic can be inspected, logged and controlled based on source, destination, service, application or user context.
Lateral movement is the process attackers use to move from one compromised system to other systems inside the network, often searching for credentials, shared drives, servers and high-value data.
Segmentation can limit ransomware spread by blocking a compromised workstation from directly reaching servers, databases, backups and other departments unless specific access is allowed.
Micro-segmentation applies access controls around individual workloads or servers, even inside the same broad network zone. It helps control east-west traffic between systems.
Guest wireless, IoT devices, printers, management systems, backup systems, databases, servers and DMZ services should be separated based on trust level and business purpose.
Teams should monitor inter-VLAN traffic, firewall allow and deny logs, authentication logs, failed access attempts, internal scanning, traffic anomalies and policy violations.
SUSAN can help teams connect segmentation findings, remediation ownership, control evidence and audit readiness into a structured GRC and continuous assurance workflow.
Reduce Lateral Movement with Stronger Network Segmentation
A flat internal network gives attackers room to move. Strong segmentation with VLANs, firewalls, default deny rules, inter-zone logging and regular policy review helps contain compromise before it becomes a full-network incident.
ServQual can review your VLAN design, firewall policy, east-west traffic controls and segmentation governance to identify flat network exposure and lateral movement paths. Explore ServQual Cybersecurity Services or contact ServQual to move from static segmentation diagrams to continuous, audit-ready assurance.
Disclaimer: This article is provided for general informational and educational purposes only and does not constitute professional security, legal or compliance advice. Network segmentation designs vary by organization, environment and risk profile. Readers should assess their own requirements and consult qualified professionals before implementing changes. ServQual makes no warranty regarding completeness or suitability for any particular purpose and accepts no liability for actions taken based on this content.